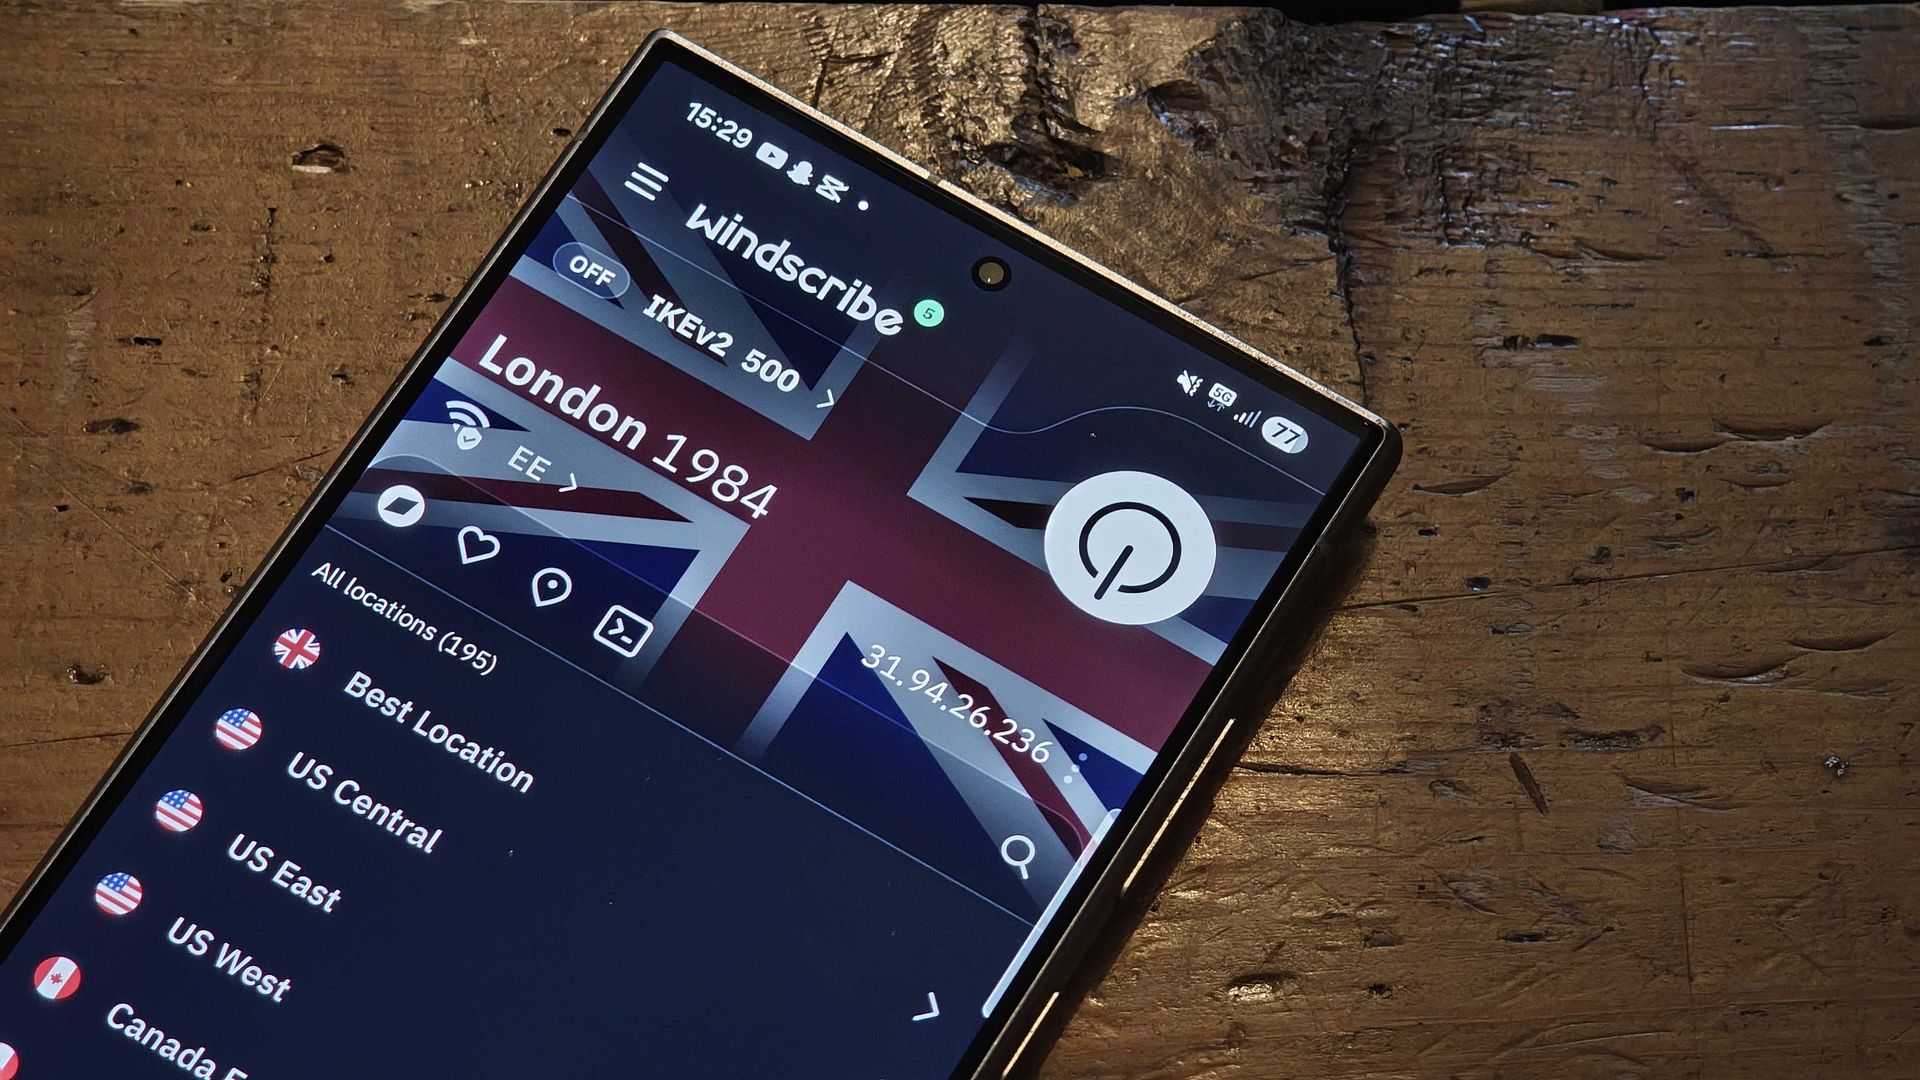
- A Windscribe update from July 2026 appears to credit AI engine Fable for identifying necessary fixes
- The AI audit successfully spotted complex vulnerabilities across the provider's Windows, macOS, and Linux applications.
- Rival providers remain seriously apprehensive of the technology, warning of the possible consequences of error.
Windscribe appears to have quietly revealed that it used artificial intelligence to audit its software.
Hidden within the changelog for release 2.33.11, deployed on July 6, 2026, the company mentions that the update includes security fixes stemming directly from an AI review by Fable 5, an advanced AI model developed by Anthropic.
Should this be true, it’d be the first instance of a commercial VPN provider relying on a large language model to conduct a comprehensive security evaluation of its core infrastructure.
What did the Fable 5 audit find?
A closer look at the release notes shows that the Fable 5 audit successfully identified highly technical areas for improvement, helping developers secure the app against potential local attacks and data leaks.
According to Windscribe, the update includes "App hardening from the Fable 5 audit, including WireGuard key validation, Control D API key log redaction, IPC exposure hardening, safer logging, installer argument redaction, and package/dependency handling fixes."
In simpler terms, the audit identified several ways to secure how the VPN handles encryption keys for the popular WireGuard protocol and ensure that sensitive API keys aren’t accidentally saved in the software's error logs.
It also identified how Windscribe could tighten up how different parts of the application communicate with each other (known as IPC exposure), which stops bad actors from exploiting the app locally on your device.
The changelog also lists a staggering number of accompanying fixes deployed in this same update. Windscribe patched a "DLL planting vulnerability" in its Windows bootstrapper, a flaw where malicious code could be loaded in place of a legitimate file, and resolved a local privilege escalation vulnerability on Linux.
Will AI replace human audits?
Historically, VPN providers undergo independent, third-party audits to prove they do not keep logs of user activity or harbor hidden security flaws.
While an AI like Anthropic's Fable 5 can process vast amounts of code rapidly, its use raises new questions about transparency.
Can an AI audit provide the same level of assurance as a human expert? Rival providers are highly skeptical about completely handing the reins over to machines.
Speaking to TechRadar, Tomas Stamulis, CSO at Surfshark, explained that while the company uses AI models internally to spot vulnerabilities "at a scale and speed impossible for humans," formal public audits still require a human touch.
"We currently rely on independent, qualified auditors, such as Deloitte or Cure53, for our formal audits," Stamulis told us. "We strongly believe that independent validation requires external human oversight to maintain contextual analysis and ensure reliability."
Stamulis warned that relying entirely on an AI for external validation carries unique risks, particularly regarding how these language models are fed information.
He noted that "given the risk that AI findings could be manipulated through context and prompting, human-led independent oversight remains the only way to provide the level of contextual analysis and manipulation-proof assurance that authorities and customers expect."
We are still waiting to hear back from Windscribe regarding their decision to prioritize an AI-driven approach for this specific update.
However, as the industry continues bolstering protections against advanced threats, AI auditing, whether used internally or publicly, represents the next major evolution in digital privacy.


